Role-scoped workspaces
Operational views are checked against the signed-in user, business and role before private data is returned.
JOJO CONNECT is designed so an operator works inside its own authorised workspace, while JOJO Technologies administration and finance roles have access only where their operating responsibility requires it.
This page explains current product controls. It is not a substitute for contractual terms or an independent security assurance.
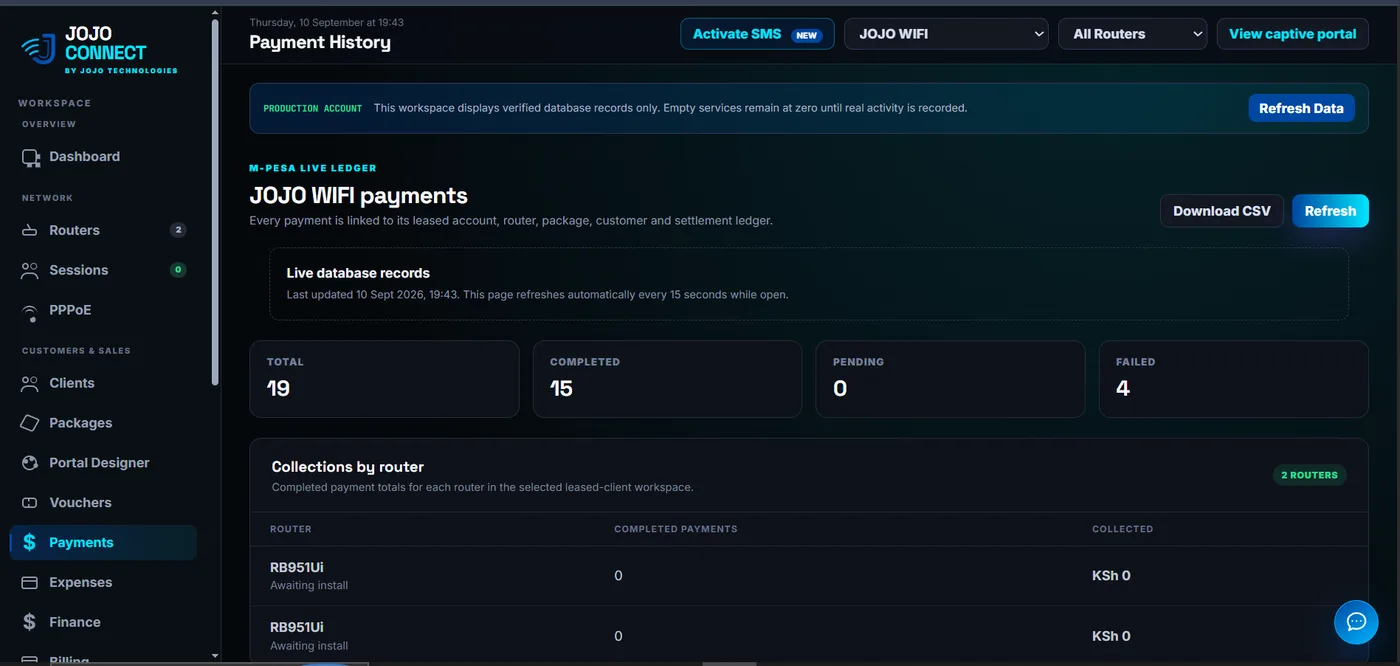
Operational views are checked against the signed-in user, business and role before private data is returned.
Leased operators see their own routers, hotspot users and records—not another operator’s workspace.
Customer identity and financial detail are available only to authorised administrative and finance roles.
Operational controls, settlement decisions and material support actions retain an audit trail.
Authentication, verification and sensitive actions are deliberately kept separate from public pages and the isolated demo.